Build · DORA 90-Day Programme · EMI · PI · CASP
From gap to audit-ready
in ninety days.
One named owner for ICT risk, operating controls and the evidence your supervisor expects, through the ninety days. Fixed scope, fixed price. The artefacts stay with you.
€15-40K one-time · Fixed scope, fixed price · Typically 2-4 hours a week of your team
Ninety days. Three stages. One owner.
Weeks 1-2Diagnosegap analysis and roadmapOwner · CyAdviso
Weeks 3-10Buildbuild and implementOwner · CyAdviso
Weeks 10-12Validatetest and validateOwner · CyAdviso
Beyond day 90If retainedongoing ownership, a separate engagementOwner · CyAdviso
EMIPayment InstitutionCASP
€15-40Kone-time · fixed scope, fixed price
90 daysDay 1 to Day 90, then a boundary
2-4 hoursa week of your team, typically
CyAdvisonamed ICT-risk owner, Day 1 to Day 90
Who the programme is for · EU and UK financial-sector supervision
For EMIs, payment institutions and CASPs
that have to run DORA, not read about it.
01 · The triggerA letter arrivedA supervisor letter or inspection notice has put DORA on the CEO's desk.
02 · The gapNobody is namedCompliance owns AML, the CTO owns systems; nobody owns ICT risk.
03 · The workIt exists in piecesPolicies, a supplier list, a pen-test PDF: work a supervisor cannot read end to end.
One named owner for ninety days. The operating system built, validated and left named on your side.
Management-body accountability remains. National law and licence conditions apply.Not the right fitCompanies outside financial regulation, or a paper audit without controls that run.
The programme · Day 1 to Day 90
Three stages. One owner.
A boundary at day 90.
CyAdviso · named ICT-risk ownerDay 90Ownership can continue, if retained
Day 1
Weeks 1-2
Diagnose
What applies to your licence and providers, and what is missing.
- Gap analysis against DORA obligations
- Gap register, rated per obligation
- Remediation roadmap with owners
- Board-ready summary
Your teamPolicies, contracts, incident records; review of the gap register.
OutcomeGap register and roadmap, owners named
Weeks 3-10
Build
Build the operating controls and the evidence structure a supervisor reads.
- ICT-risk framework and policy pack, for board approval
- Register of Information
- Incident classification and notification workflow
- Testing plan
- Evidence pack for external review
Your teamReviews as drafts arrive; the board approves the framework.
OutcomeFramework, Register, incident workflow, evidence pack
Weeks 10-12
Validate
Exercise the controls and bring the evidence current.
- Resilience testing
- Tabletop and incident-response drills
- Evidence index brought current
- Handover to a named internal owner
Your teamDrill participation; confirm the owner from day 91.
OutcomeDrill records, current evidence index, handover
Typically 2-4 hours a week of your teamFixed scope · fixed priceProgramme ends at day 90
Ownership during the programme
What CyAdviso owns.
What stays with you.
Ownership of ICT risk is named for the ninety days. Accountability is not transferred: it stays with the management body, as DORA requires.
CyAdviso · named ICT-risk owner · Day 1-90Accountability · management body · remains
CyAdviso ownsDay 1-90
- ICT risk as a whole, named
- Framework, registers and workflows: drafted and implemented
- Testing, drills and their records
- The evidence structure a supervisor reads end to end
Stays with youThroughout
- Management-body accountability under DORA
- Approval of the framework and policies
- Named internal owners for remediation items
- Provider contracts and relationships
- Operation of your own systems
Outside the programmeSeparate engagements
- Ownership after day 90: the vCISO Retainer
- Independent assessment, for SWIFT CSP or PSD2 SCA, never on controls we built
- Requirements beyond the agreed scope
Day 90 is a boundary. The programme ends with its artefacts delivered; ongoing ownership is a separate engagement.
Management-body accountability remains. Where national law or licence conditions set further requirements, they apply.
A defensible floor, not a promise of what a reviewer will find. No engagement guarantees a supervisory outcome.
Independence rule: we do not independently assess controls we have built. Where an independent assessment is required, it is a separate engagement.


Day 90 · what exists
What your supervisor can read on day 90.
Each is a control, a register or a record that runs, and the evidence that it does.
Delivered by the programme
Gap register and roadmapDiagnosePriorities, owners and the remediation path.
ICT-risk frameworkBuild · board-approvedGovernance and policies the management body adopts.
Register of InformationBuildICT third-party arrangements in supervisory format.
Incident workflowBuild · exercised in ValidateClassification, escalation and notification process.
Testing and drill recordsValidateThe plan, and evidence that exercises happened.
Evidence indexCurrent at day 90What exists, where it sits and when it was reviewed.
Board Reporting Pack shown as an example format; it is maintained under the vCISO Retainer. Artefact images are reconstructed excerpts with placeholder values.
Why CyAdviso operates it
“The regulator stopped repeating the same control questions.”
“We had fragmented evidence and couldn't explain our controls under review. Within 90 days, our framework was documented, defensible, and the regulator stopped repeating the same control questions.”CEO · EU-licensed EMIRead the EMI case →
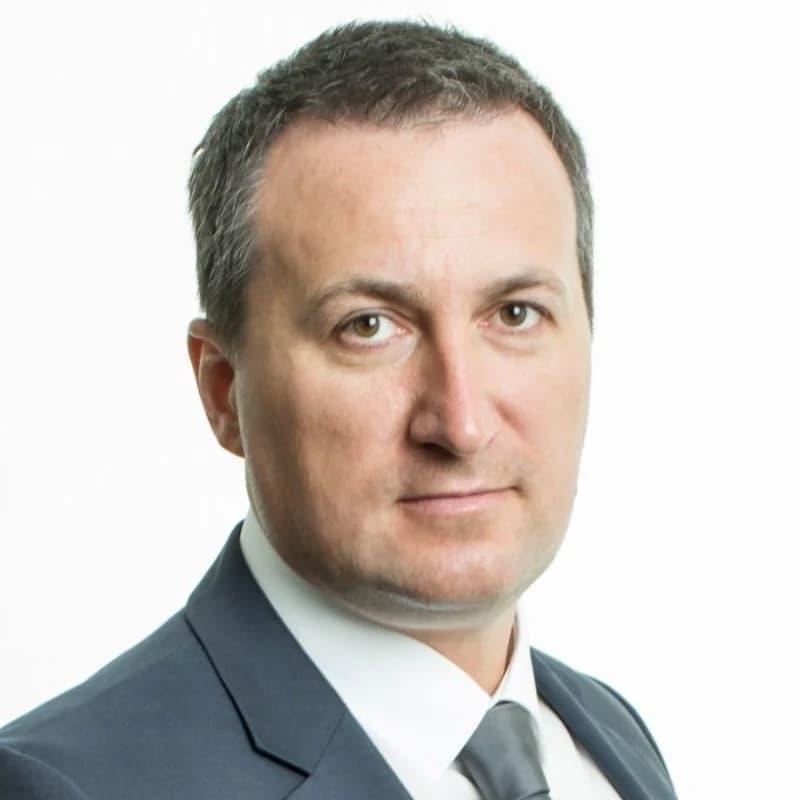
Who holds the seat
Andrey Gubarev, founder and vCISO. CISO since 2008; former CISO at EU and UK-licensed financial institutions.
CISM · CDPSE · SABSAAbout CyAdviso →Independence rule: we do not independently assess controls we have built. Where an independent assessment is required, for SWIFT CSP or PSD2 SCA, it is a separate engagement.
The decision
One fixed price.
One owner through day 90.
Fifteen minutes to scope the programme for your licence and your providers.
info@cyadviso.com · SIA CyAdviso · Riga, Latvia · EU